How to Build a 90 Day AI Roadmap Without Breaking HIPAA
A rushed AI roadmap is how HIPAA violations happen. Here is how to sequence a 90 day plan that ships fast without cutting compliance corners.
This is some text inside of a div block.
A rushed AI roadmap is how HIPAA violations happen. Here is how to sequence a 90 day plan that ships fast without cutting compliance corners.
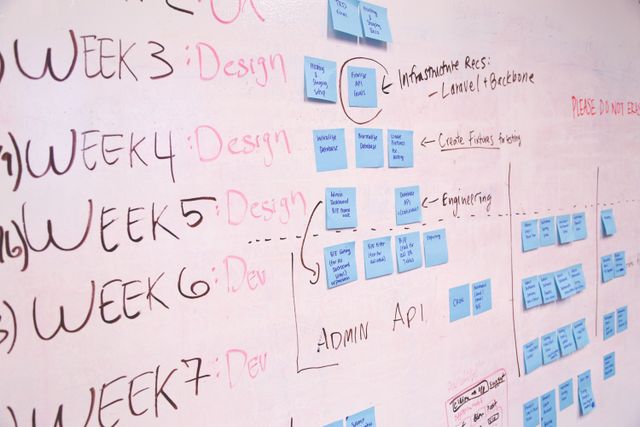
Most AI roadmaps get built around what a team wants to ship, then compliance gets slotted in wherever it fits. That order produces roadmaps that look ambitious on a slide and fall apart the moment a feature actually needs a signed BAA, a completed risk analysis, or a data flow nobody mapped in advance. A 90 day roadmap that survives contact with HIPAA has to be built the other way around.
A roadmap usually stalls not because the ideas were bad, but because compliance work that should have happened in week one gets discovered in week eight, right as a feature is supposed to ship. Risk analysis failures were the most common violation cited in HIPAA enforcement actions in 2024, which reflects how often this exact gap goes unaddressed until it becomes a real problem. A roadmap that treats compliance as a final check before launch, rather than a structural part of the plan, is building the same gap into its own schedule. The pattern tends to repeat itself feature after feature once it starts. A team ships an AI summarization tool, discovers mid launch that the vendor agreement does not cover the specific endpoint in use, pauses to fix it, and then repeats a version of the same discovery on the next feature because nothing was actually built to prevent it from happening again. A 90 day roadmap that front loads this work once, at the start, breaks that cycle instead of running through it on every feature individually.
The first two weeks of any real AI roadmap need to answer questions the rest of the plan depends on. What AI features are already running in production, and does each one have a signed BAA covering the specific service and configuration in use? Where does PHI actually flow once AI is in the loop, including in retrieval systems and embeddings that rarely make it onto an architecture diagram? Is patient data structured well enough to support what the roadmap assumes, or does it need cleanup first? Skipping this phase does not remove the risk hiding in the answers. It just delays discovering it until later, when fixing it costs more and blocks more of the plan behind it.
Whatever surfaces as an active compliance gap in the first phase needs to move to the front of the roadmap, ahead of new feature work. An AI vendor relationship with no BAA, a misconfigured retention setting, a data flow that mixes HIPAA only data with substance use disorder records without segmentation, these are not backlog items. They are active exposure, and a roadmap that keeps building new features on top of them is compounding risk rather than managing it. This phase is usually where the most uncomfortable findings surface, since it means confronting gaps that may have existed quietly for months.
With the urgent gaps closed, the roadmap can turn to the features it was actually meant to deliver, sequenced against both business priority and technical dependency. Infrastructure work, a missing data layer, a vector store that needs proper access controls, tends to need to land before the features that depend on it, not alongside them as an afterthought. Team readiness matters here too. A roadmap that assumes engineers already know how to test AI generated code for the specific ways it fails, or how to scope a BAA against the exact service being used, tends to slip its own timeline once that gap becomes apparent mid build.
Shipping a compliant feature and being able to demonstrate that it is compliant are two different things, and a 90 day roadmap needs to produce both. That means the risk analysis gets updated to explicitly cover each new AI data flow as it ships, not batched into an annual review months later. Audit logging needs to capture AI feature usage from day one, not retrofitted after a customer asks for it. And documentation describing what the AI actually does needs to stay accurate as the roadmap evolves, since an inaccurate disclosure compounds any issue that surfaces later far more than an accurate one would.
A behavioral health platform with two AI features already live decides to formalize a roadmap for the next quarter. The discovery phase turns up a summarization tool whose vendor agreement never explicitly extended to a beta endpoint the team started using a few months back, and a chatbot whose embeddings pipeline stores transformed session note content with no clear retention policy attached to it. Neither issue is catastrophic on its own, but both would have quietly compounded if three more features had shipped on top of them before anyone looked closely. Fixing both takes the first three weeks. The remaining nine weeks go toward the two new features the roadmap actually set out to build, now sequenced on a foundation that will not need to be revisited every time something new ships.
Our AI Acceleration Sprint follows almost exactly this sequence, front loading the discovery and urgent fixes into the first two weeks, then spending the remaining weeks building the prioritized roadmap and the compliance evidence to support it. The structure matters more than the specific calendar. A roadmap that tries to build features and discover compliance gaps at the same pace tends to do both badly, while one that sequences discovery first tends to move faster overall, not slower, because it stops rediscovering the same risk repeatedly at each new feature.
Cost varies with scope, but a useful way to think about it is against the alternative. A rushed roadmap that skips structured discovery often ends up paying for the same work twice, once quickly and incompletely during the original build, and again more expensively when a customer's security review or an actual gap forces a second pass. The second pass also tends to happen under worse conditions, mid sales cycle or after an incident, rather than on a schedule the team controls. Our pricing page breaks down what a structured 90 day engagement includes against that comparison.
Do we need to pause all feature work while we fix compliance gaps? No. Active exposures should move to the front of the queue, but most compliance work can run alongside feature development rather than blocking it entirely, as long as the sequencing is deliberate.
How is this different from a general product roadmap? A general roadmap sequences features by business value. A roadmap built around AI and HIPAA has to sequence compliance discovery and remediation first, since building on top of an undiscovered gap just makes that gap more expensive to fix later. Our FAQ page covers a few more of these distinctions.
What if we already have some AI features in production without this kind of roadmap? That is the most common starting point, not an unusual one. The discovery phase works the same way whether it happens before a first AI feature ships or after several already have, it just means the fix phase has more to address.
Can our own team build this roadmap, or do we need outside help? A strong team can build much of it internally. Outside help tends to pay off most in the discovery phase, where knowing what to look for and recognizing common gaps across many AI healthcare stacks shortens the process considerably.
Resolve Health Tech builds 90 day AI roadmaps in exactly this order, discovery first, urgent fixes second, prioritized build work last. Contact us to start yours on the right sequence.
Sana is a Technical Content Specialist at Resolve Health Tech. She specializes in breaking down complex architectural patterns, nearshore hiring trends, and software engineering workflows into actionable, human-friendly guides. Working alongside Resolve Health Tech's tech team, Sana ensures every piece of content is both highly readable and technically precise.